Impredicative: an object is defined by quantifying over a collection that contains it. R = \{x : x \notin x\} is such a definition — the condition ranges over all sets, and R would be one of them.
1908
forbids it by restricting
so you may form
x ∈ x is
Zermelo
what exists
\{x \in A : x \notin x\}, never \{x : x \notin x\}
well-formed, and false
Russell
what may be said
neither: x \notin x is not a formula
no statement at all
Zermelo's set is harmless: R = \{x \in A : x \notin x\} gives R \notin R, hence R \notin A. No set contains all sets.
Mathematics went with Zermelo, proof assistants with Russell.
Hilbert's programme, 1917
David Hilbert
Fix the language, fix the rules. A proof becomes a finite string, and checking it is a question about symbols.
Consistent? — no contradiction follows from the axioms.
Complete? — for every statement, it or its negation follows.
Decidable? — a procedure settles which of the two.
Hilbert wants all three.
Gödel, 1929 and 1931
Kurt Gödel
First-order: quantifiers range over the elements of one domain, never over its subsets — so "every bounded set of reals has a supremum" is not first-order.
Gödel
about
result
1929
first-order logic
complete: valid in every model is derivable
1931
any theory containing arithmetic
incomplete: some truth about ℕ is neither proved nor refuted
Lean quantifies over types and propositions. 1929 does not apply.
1936: the Entscheidungsproblem
Alonzo Church
Alan Turing
1928 — Hilbert and Ackermann: is there a procedure deciding whether a formula is provable? The Entscheidungsproblem.
1936 — Church and Turing, independently: there is none.
First they had to say what a procedure is. Turing: a tape, a head, a finite table of instructions. Church: the \lambda-calculus.
The lambda calculus
A calculus: a formal language with rules for calculating. Here: terms for functions, and one rule.
\lambda x.\, x + 1 is the function adding one. The rule is substitution, β-reduction: (\lambda x.\, x + 1)\, 3 becomes 3 + 1.
Numbers, pairs and recursion are not built in. They are written as \lambda-terms, and that is enough for everything Turing's machines compute.
Lean is this calculus with types on top:
example:(funx:Nat=>x+1)3=3+1:=rfl
Checking is not finding
Question about a statement \varphi
what the procedure must do
verdict
Does this text prove \varphi?
always halt, with yes or no
decidable
Does some text prove \varphi?
halt with yes whenever one exists
semi-decidable
Does some text prove \varphi?
always halt, with yes or no
undecidable
Rows 2 and 3 ask the same question. Only the demand differs — and that is where it breaks.
You prove. The machine checks. That split is a theorem, not a gap in today's software.
1967: Automath
Nicolaas Govert de Bruijn
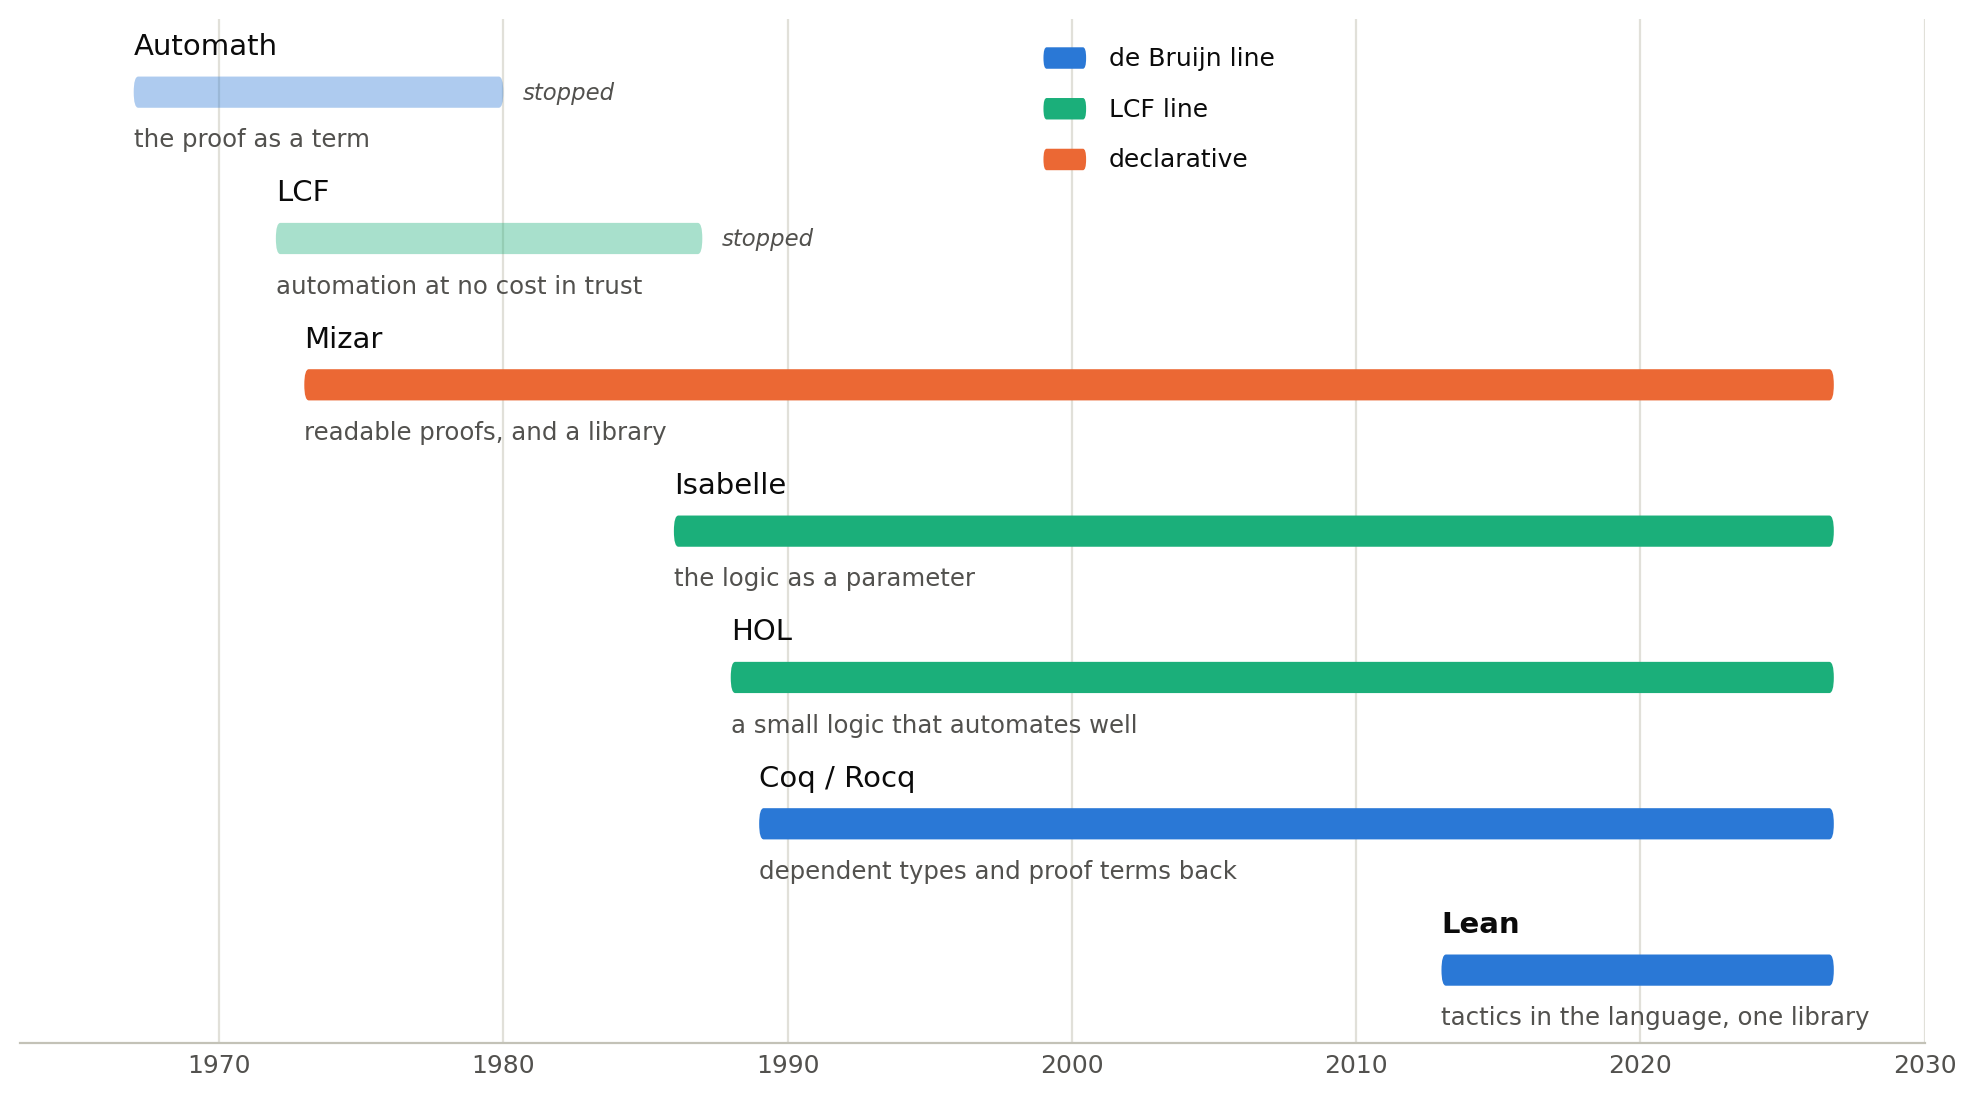
Automath — a typed \lambda-calculus with dependent types, not set theory. The first machine-checked proofs.
1977 — Landau's Grundlagen der Analysis through it, end to end.
Everything before this slide is mathematics. From here on there are machines.
The systems
Five of the seven still run. A library cannot be moved.
2013: Lean
Leonardo de Moura
2013 — Leonardo de Moura starts Lean at Microsoft Research.
2021 — Lean 4, a redesign rather than a new version.
Foundation: the Calculus of Inductive Constructions, the Automath line.
Three systems
System
Logic
Library
Lean 4
dependent types
one: Mathlib
Rocq (Coq until 2025)
dependent types
many packages
Isabelle/HOL
simple type theory
the AFP
Only Isabelle has no dependent types. Its automation is the strongest of the three.
We use Lean because Mathlib exists.
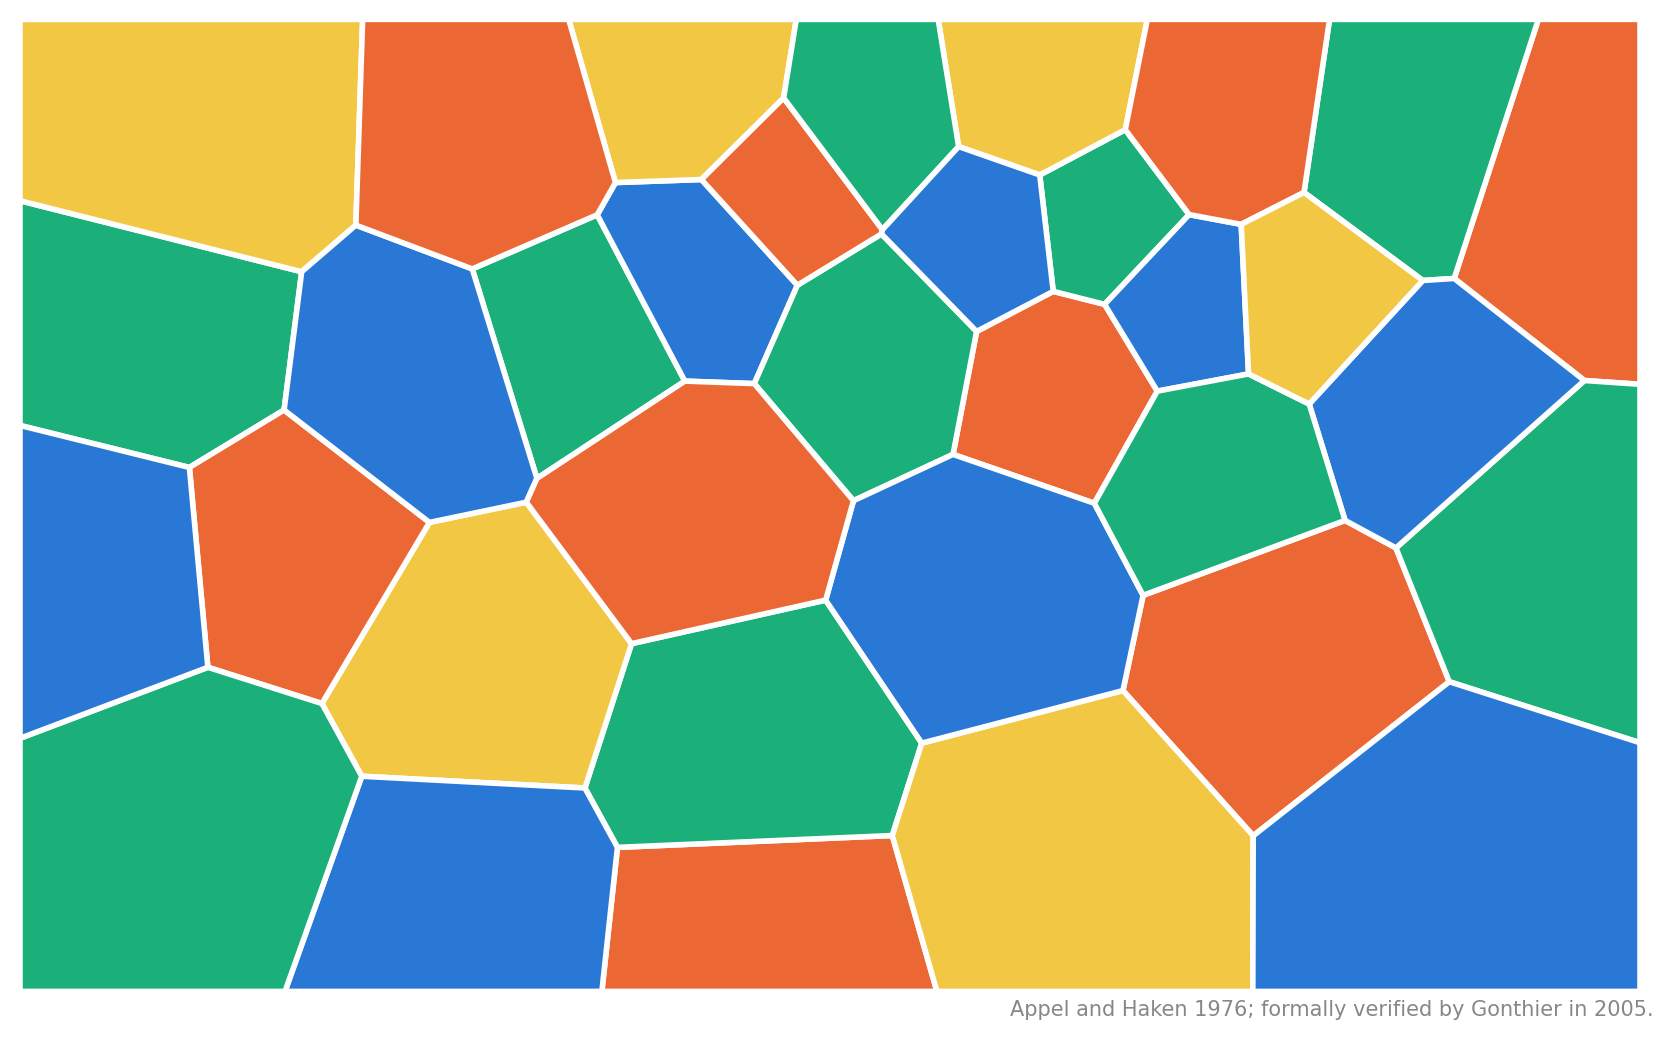
1976: the four colour theorem
Appel and Haken reduce the problem to a list of configurations, and an ordinary program checks it — no proof assistant.
No human has ever read that part.
2005: Gonthier redoes all of it in Coq, case analysis included.
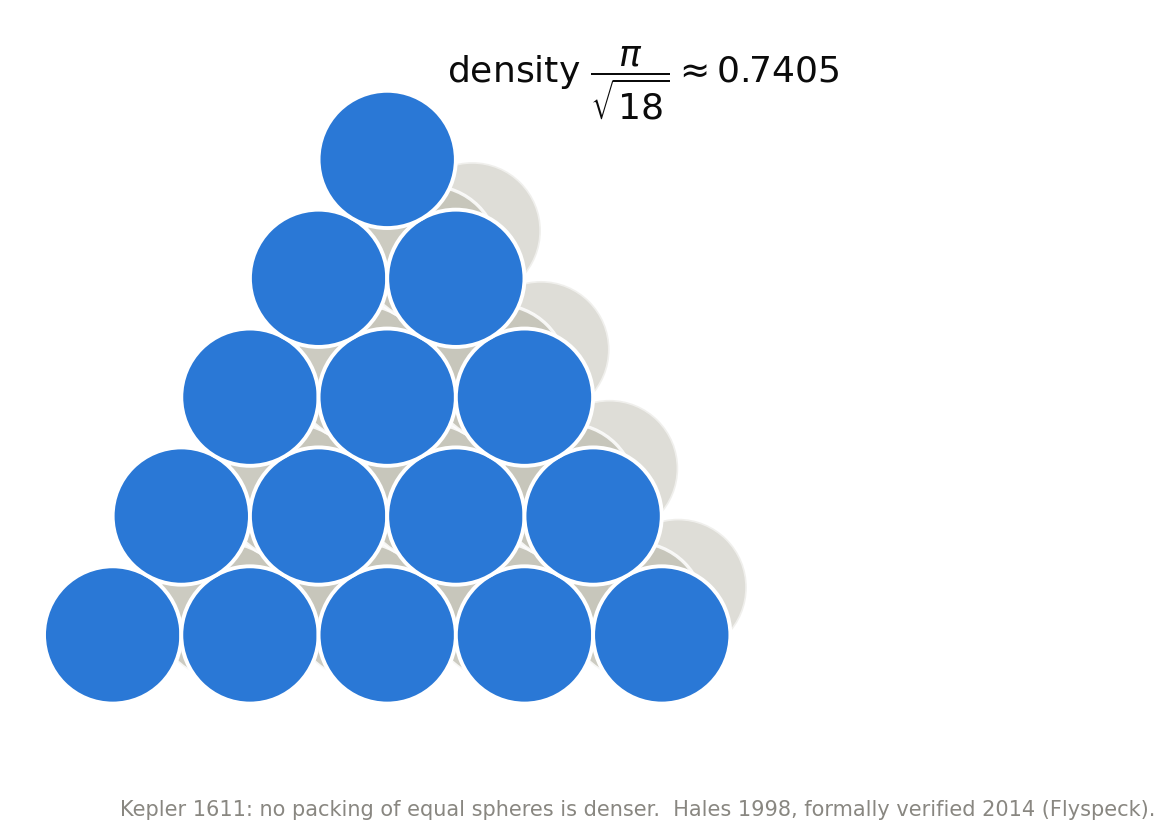
1998: the Kepler conjecture
Thomas Hales
Hales announces a proof of Kepler's conjecture of 1611. Twelve referees, four years.
Verdict: ninety-nine percent certain — and no better was possible. The Annals published it with the caveat attached.
Hales started Flyspeck. Complete formal proof in HOL Light and Isabelle, 2014.
2013: Voevodsky
Vladimir Voevodsky
1989 — Voevodsky and Kapranov identify \infty-groupoids with homotopy types.
Oct 1998 — Simpson argues that it cannot be true, but cannot say which step.
Autumn 2013 — Voevodsky accepts it and finds his own error.
Mathematics runs on a complex system of mutual trust based on reputations.
Perfectoid spaces, 2019
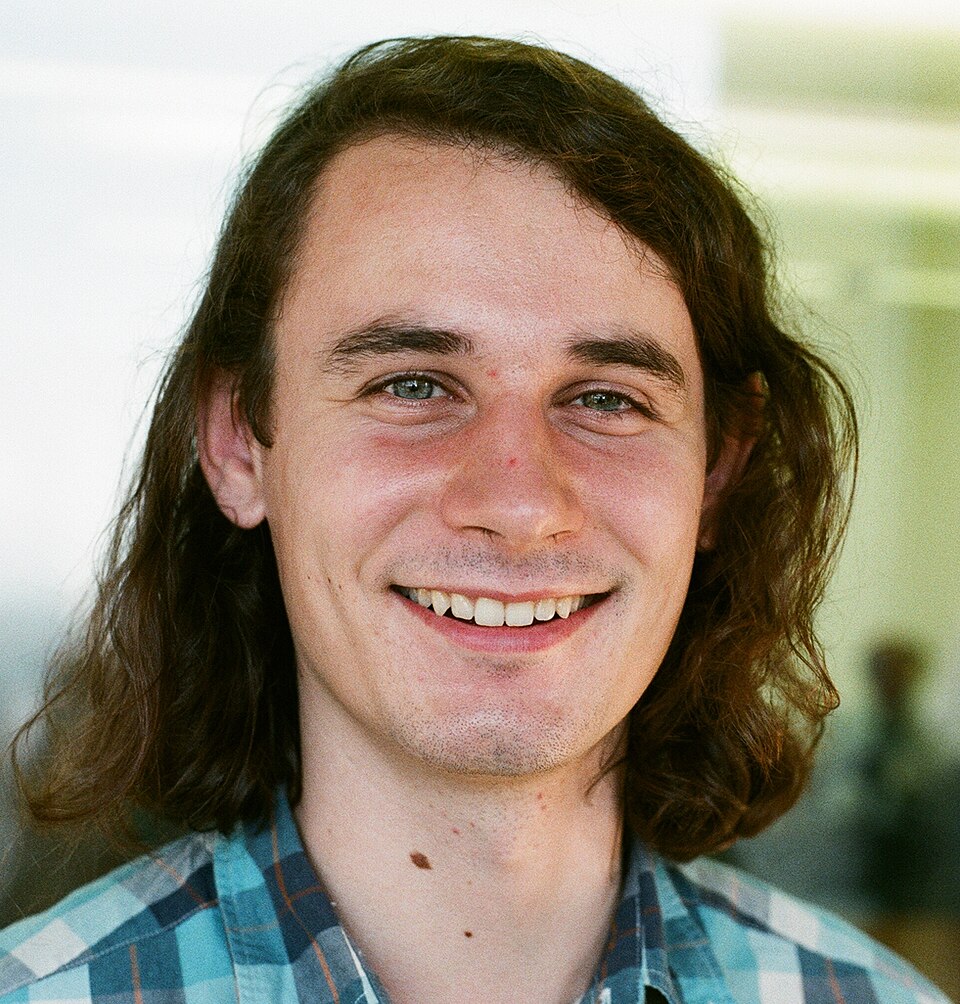
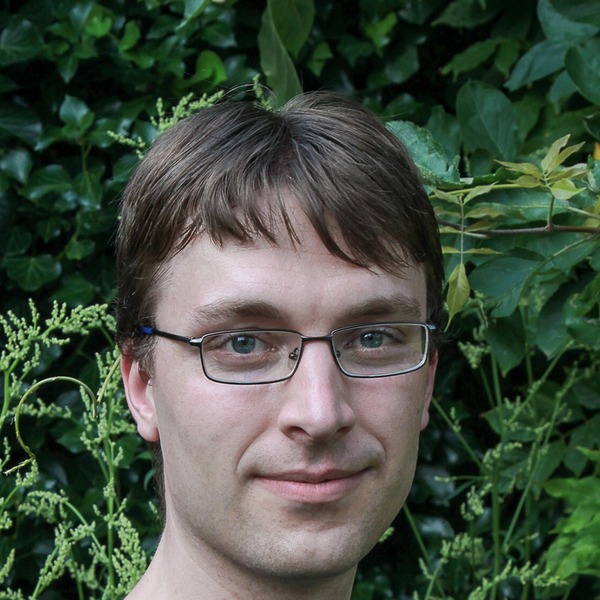
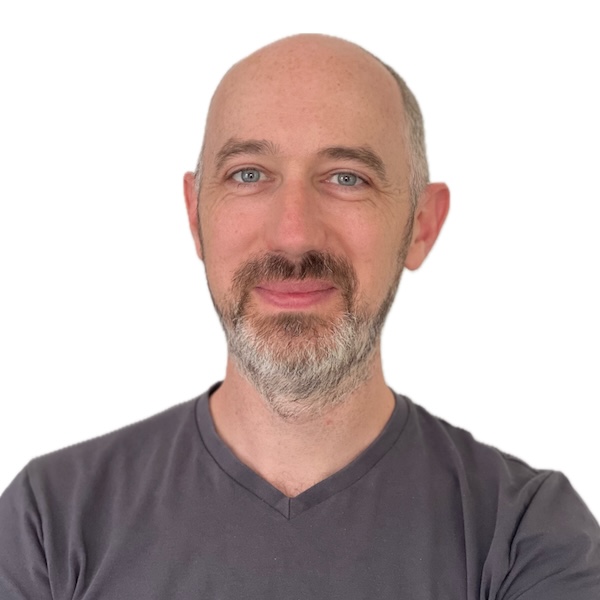
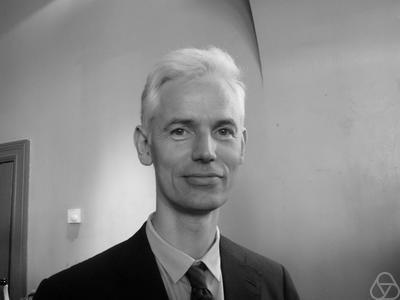
Kevin Buzzard
Johan Commelin
Patrick Massot
The problem: could an object as complicated as Scholze's perfectoid space be stated at all in a proof assistant?
They formalized a definition, not a theorem. Stating is a different problem from proving.
2020: the Liquid Tensor Experiment
Peter Scholze
Johan Commelin
Scholze posts a challenge on Buzzard's blog: a theorem in condensed mathematics he is not certain of.
Liquid Tensor Experiment, led by Commelin. Finished July 2022.
The request came from a working mathematician, not from logicians. That is what had changed.
Sphere eversion, 2022
Patrick Massot
Floris van Doorn
Oliver Nash
The problem: Mathlib had no differential geometry, and Gromov's h-principle needs it.
So they built the API first and proved the theorem afterwards. That order is the ordinary shape of the work.
Freiman-Ruzsa, 2023
Timothy Gowers
Ben Green
Terence Tao
Gowers, Green, Manners and Tao. There is no freely licensed photograph of Freddie Manners.
The problem: a formalization took one team years, so it always came long after the paper.
A blueprint cuts the work into pieces with stated interfaces. Strangers in parallel, three weeks, before refereeing.
Equational Theories, 2024-25
The problem: 22 028 942 implications between 4 694 laws on magmas. Not deep — but beyond any human team.
abbrevEquation3(a:Type)[Mula]:=∀x:a,x=x*xabbrevEquation4(a:Type)[Mula]:=∀xy:a,x=x*y-- Equation 4 implies Equation 3: take y := x.example(a:Type)[Mula](h:Equation4a):Equation3a:=funx=>hxx
Lean today
A new Lean every month. v4.34.0 on 14 September 2026, v4.35.0 on 12 October.
Nothing updates by itself. lean-toolchain names one version, elan fetches it, lake builds against it.
This course is pinned to v4.34.0 all semester.
Lean FRO — a non-profit since July 2023, nineteen people, living on donations.
Mathlib
One library, one repository, one version. Everything in this course imports it.
2.33 million lines, about 189 000 theorems, 1 031 contributors. 27 commits a day.
No stable releases. Mathlib follows Lean, your project follows Mathlib.
Reading formal statements. Judging whether a formal statement says what the informal one claims.
Interactive theorem proving. A small kernel checks every logical step of a proof, and the editor reports what remains to be proved as you write. This is not the older use of computers in mathematics, which was to work through many cases.
Mathematical content. The mathematics in the first half is deliberately easy, because explaining a proof to a computer requires understanding it first, and a proof of more than a few lines has to be planned so that the commands — tactics — fit together. The second half goes deeper into the mathematics.
Functional programming. Inductive types, structures, typeclasses and monads, needed both to use Lean and to read Mathlib.
Type theory. Lean rests on dependent type theory: the Curry-Howard correspondence, dependent types, the universe hierarchy, and Lean's axioms.
Mathematics in Mathlib. How the library organizes order theory, the algebraic hierarchy, filters (a single framework for limits), topology, measure theory and discrete probability. Textbooks rarely treat these from the point of view of formalization.
Proof engineering. Automation tactics, searching Mathlib, and the common pitfalls of a large formal library.
What your machine needs
Every sheet begins with import Mathlib, so a two-line sheet needs as much memory as the hardest one.
Resource
Minimum
Comfortable
RAM
16 GB
32 GB
Free disk
20 GB
20 GB
Disk
SSD
NVMe SSD
Below the minimum? Talk to us — there is a server with 128 GB.